Friday Keynote
Ashley Sequeira
Open to everyone, including non-military! VetSec's mission is to create a world where no veteran pursuing a career in technology goes unemployed.
Register Free The conference begins on October 22, 2026.VetSec, Inc., is a registered 501c3 non-profit based in the United States with the mission to create a world in which no veteran pursuing a career in cybersecurity goes unemployed. Utilizing a community-based approach encouraging fellow veterans to give back, VetSec has over 6,500 members in the organization. Utilizing sponsorship funding and donations, VetSec and their strategic partners provide needed training resources to help military members transition into and upskill in the cybersecurity industry. We offer resume reviews, transition advice, mentorship, and training vouchers and discounts, all thanks to our donors and partners.
Longer sessions covering a wide range of topics such as Resume Reviews, Starting a Business, VA Disability, Mental Health, and Technical training.
Learn directly from information security professionals, fellow veterans, and industry experts in short, digestible 30-min blocks.
Connect with peers in the virtual lobby and stage chat rooms, then stick around for Trivia and Who's Slide Is It Anyway at the end of the day.
Friday, Oct 23
[TBA]
Speaker Bio and photo coming soon!
Saturday, Oct 24
From the Air Force to the startup world: lessons learned along the way
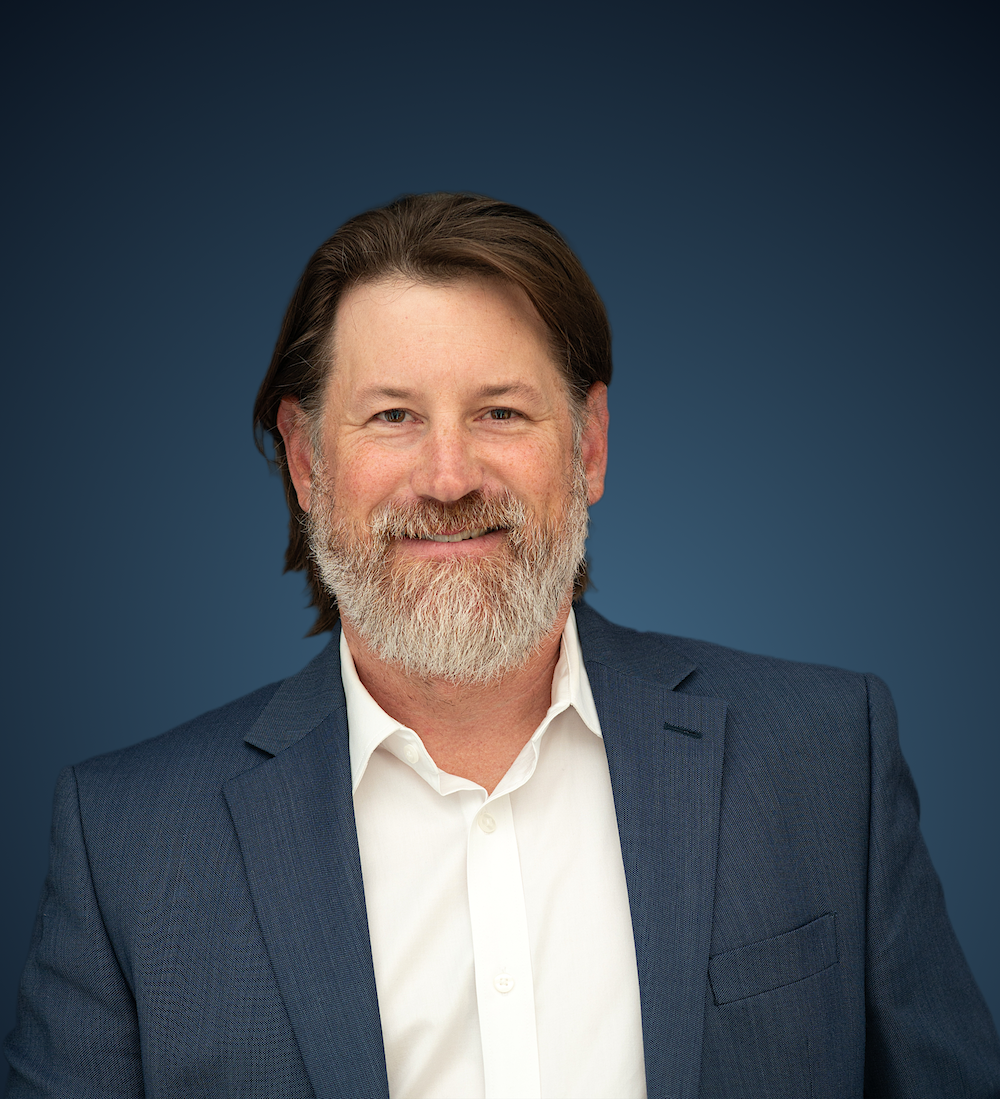
Vince Crisler began his cybersecurity career in the US Air Force, commissioned on December 7, 2001, and separated as a Captain in 2008. The Air Force took him from running networks at Ramstein Air Base to the Pentagon's National Military Command Center to the White House, where he served as Chief Information Security Officer for the Executive Office of the President and built the White House's first 24x7x365 security operations center. After government service he co-founded Dark Cubed, raised more than $10M in venture funding, earned two US patents, and led the company to its acquisition by Celerium, where he serves today as Chief Strategy Officer and CISO. The Dark Cubed platform was selected by the DoD Cyber Crime Center to protect defense contractors. He is a director of SCI Engineered Materials and co-founder of Motherwell Distilling.
Please use the buttons below to switch between dates.
John Stoner + Tyler Hardy
Marcelle Lee | Founder and Principal Advisor at Fractal Security Group
Description coming soon.
Laruen Howard & Natasha
Description coming soon.
Tom Marsland | Former VetSec Chairman, Senior Director of Security Operations at DigiCert
Tom's VA Disability Workshop provides a practical, step-by-step guide for veterans navigating the VA disability claims process and maximizing their earned benefits. He demystifies the connection between active-duty service records and claim approvals, emphasizing the crucial role of thorough medical documentation before separation. Beyond federal disability compensation, the talk highlights lesser-known state and county-level perks, including property tax exemptions and educational benefits for dependents. Tom also outlines how to enroll in and utilize VA healthcare effectively alongside existing coverage like Tricare. The session concludes with actionable advice on tracking conditions over time and leveraging community resources to successfully manage ongoing claims.
John Stoner | Senior Technical Instructor at Mandiant (Google)
Ready to supercharge your threat intelligence game? Welcome to the ultimate Mandiant Cyber Threat Intelligence (CTI) Crash Course! In this high-octane 4-hour workshop, we are stripping away the fluff and diving straight in.
Whether you are a Blue Teamer, SOC analyst, or cybersecurity enthusiast, this official Mandiant workshop is designed to transition you from reactive to proactive! We’ll kick off by breaking down the CTI Lifecycle, learning how to turn raw, chaotic info into timely, relevant, and actionable intelligence.
Zobes
VetSecCon trivia is a pub-style trivia consisting of 8 categories across 4 rounds. There will be a wide spectrum of categories, including, but not limited to, cybersecurity, notable events, military knowledge, nostalgia trips, and potent potables. Grab your friends and play along in this completely free, fully online, “sure to be a wacky time” trivia event.
John Stoner + Tyler Hardy
Philip Wylie | Chief Security Evangelist and Senior Consultant at Suzu Labs
Tyrone Wilson | Founder & CEO of Cover6 Solutions
Every veteran leaving the service hits the same wall: no job without experience, no experience without the job. A lab is how you go around it.
You'll leave knowing what to build, how to use it to answer interview questions you can't fake, and how to turn it into paying work.
Bradley Evans (Squelch) | Founder of competitive cybersecurity teams at University of California
If you’re just getting started out in cybersecurity, you’ve probably heard of CTF. SANS NetWars! CTFTime! CCDC! DEF CON CTF! picoCTF! This talk will discuss what CTFs are, describe some major CTFs in major skill domains and their skill levels, how to participate, and talk about what you can expect when you play. We’ll go over forming a team and some general strategies. We will also discuss why it’s worth your time and what you could get out of participating. AI hasn’t killed CTF, it just altered the game and lowered the barrier to entry.
Samuel Wong | DoD Security Researcher
People spend lots of time and money on their resumes - a lot of people agree that optimizing your resume is a good use of time with a great return. But a resume is just the first part of the “exploit chain” before you land the “shell” (Job). In this presentation I will present the case for spending at least as much time optimizing and honing your interview skills, and recommending some simple resources that you can take advantage of to that end. We’ll have some fun by pointing out the analogies of a job search and a CTF as well - as it turns out, the same technical skills you’ve been grinding are very transferable to the job hunt.
Crystal Morin | Senior Cybersecurity Strategist at Sysdig
Threats were once measured in days, weeks, and months, but those days are over. Today, with attackers weaponizing AI and automating operations, vulnerabilities are exploited within hours of disclosure and attacks unfold in minutes. Just in the first half of 2026, the Sysdig Threat Research Team (TRT) discovered AI agents running entire attacks end-to-end — no human at the keyboard.
This talk breaks down four ways that agentic AI has fundamentally changed what defenders are up against: autonomous agentic threat actors that pivot from access to exfiltration in under an hour, AI infrastructure itself as a prime target (and credential goldmine), disclosure-to-exploitation timelines collapsing to single-digit hours, and attackers jailbreaking and using guardrail-stripped “abliterated” LLMs. With real-world cases like JADEPUFFER, attendees will explore what these attacks look like in the wild, how to detect them, and what security teams need to change to keep pace with attackers that never stop working.
Ashley Sequeira
Mark Schober | Founder at Blue Cape Security
Laura Khalil | Professional Dungeon Master, Founder at Once Upon a Roll
Every security team is an adventuring party. The question is whether you know what kind.
In this session, professional Dungeon Master Laura Khalil uses the D&D class system as a lens for how we show up under pressure. What archetype do you bring to work? Are you an “Oops, All Barbarians” team, charging into every decision like it's a breach at 2am? Or is your party built to survive whatever the campaign throws at you?
In a world of AI-driven change and incidents that never wait for business hours, knowing your party composition is how effective teams respond to crisis.
Bryson Bort | Founder at SCYTHE and GRIMM, Co-Founder of the ICS Village
You’re not crazy, you just want to start your own company, which takes a little crazy to pull off. This talk covers the realities of entrepreneurship, from ideation and startup phases to choosing a business model, raising capital, investors, legal requirements, working with friends, market sizing, pricing, economics, and back-office challenges. Along the way, I’ll share lessons from my own experience starting several companies!
Kirsten Renner | Founder at Dynamic Talent Solutions LLC and HireSummit.io
In this 30-minute session, longtime talent executive and recruiter Kirsten Renner takes you behind the scenes of how employers build offers, what may actually be negotiable, and how to advocate for yourself without jeopardizing an opportunity you're excited about.
Because negotiating power starts long before an offer arrives, we'll cover practical interview strategies, follow-up techniques, closing questions, and ways to translate military experience into business value.
Joe Marshall | Senior IoT Security Strategist at Cisco Talos Intelligence Group
Burnout. Cybersecurity has used that one word for what this work does to people, and it's the wrong word for most of it. Burnout is workload injury and rest fixes it. Secondary traumatic stress, vicarious trauma, and moral injury are different injuries with different causes, different signals, and different fixes, and none of them respond to time off.
This talk borrows a solution the military built decades ago. Combat and Operational Stress Control doctrine gives us a four-zone continuum: Ready, Reacting, Injured, Crisis to ID and respond to stress. And Stress First Aid gives us a peer-deliverable protocol that requires no clinical license to run.
I'll walk the four injuries, show how the continuum maps onto SOC, DFIR, threat intel, and security practitioner roles, and hand you a two-page playbook and larger framework you can use right away.
Shawn Fuss | Sales Engineer at Fortinet
In July 2026, the Fortinet Training Institute updated its curriculum to feature new industry-recognized certification paths and enhanced vendor-agnostic and product-specific training materials. Today, we will walk you through these updates and explain how you can leverage the VetSec Community to access the platform.
John Stoner + Tyler Hardy
John Stoner + Tyler Hardy
Gabe Jaggi | Sales Engineer at Palo Alto Networks
The world of sales is not all cold calling and maintaining an extensive contact list. It’s also not nearly as scary as it might seem. Did you learn how to succeed in sales without even knowing it? Are you reading low salaries on job postings and thinking it isn’t for you? I’m going to explain what a technical sales engineer is and whether it is for you.
Drew Hjelm | Founder at Helm Information Security
Health-ISAC's July 2026 advisory on ShinyHunters made the pattern explicit: SSO is the control plane, and a single social-engineered password reset gives an attacker a valid session and a directory of every SaaS app your identity provider can reach.
This talk breaks the attack chain into five gates an intruder must clear in sequence: the help desk, device trust, network restrictions, standing access, and detection. Most breaches succeed not through one brilliant move but because they luckily made it through all five gates.
Using concrete configuration detail from Okta, Entra ID, Salesforce, Snowflake, and Databricks, this session shows what closing each gate actually means, which controls are free and which are gated behind a license tier, and why network restrictions and audit logging are frequently procurement decisions disguised as engineering ones.
Cody Ronk | cybersecurity sales professional focused on the public sector
Veterans are often told to polish their resume, earn certifications, and apply to as many jobs as possible. But an effective job search looks much more like a sales campaign.
This talk teaches veterans how to use practical sales skills to identify target companies, find the right people, write better outreach, build relationships, and separate yourself from the pack. A major focus will be how veterans can use their free year of LinkedIn Premium to research companies, expand their network, reach hiring managers and industry professionals, and build a repeatable job-search pipeline.
Attendees will leave with a simple framework for targeting, prospecting, messaging, networking, and follow-up that they can immediately apply to cybersecurity and technology job searches.
Daniel Rogers (sp0r!um) | Security Engineer
This talk dissects a real-world help desk impersonation attack, breaking down the full attack chain, the malware used, and the discovered IoCs. Key takeaways include learning how to analyze malware, extract IoCs, and how to build IoCs from those IoCs (as generic as possible).
Andrew Schoka | CEO & Co-Founder of Hardshell
AI security is hiring the way cloud security was hiring in 2012. The roles (and need) are real, but the titles aren't standardized, no cert matters yet, and most hiring managers are improvising. For veterans, that's good news. This field rewards demonstrated work over credentials, and military backgrounds map into it directly. This talk gives a working map of AI security's sub-fields, shows where cybersecurity, intel, and data backgrounds transfer, then lays out a plan for making the move into the career field while it's still being built out. I'll bring both the hiring-manager view from running an AI security startup and the transition view from making this exact jump out of Army offensive cyber.
Vince Crisler
Capt(Ret) Steve Waterhouse, CD | Cybersecurity Consultant and Speaker
As one of Canada's first “cyber-soldiers,” I transitioned from training combat troops in the Royal 22e Régiment to becoming the first Information Systems Security Officer at CFB Montreal and the Royal Military College Saint-Jean — then rose to Assistant Deputy Minister of Government Information Security and Cybersecurity for Quebec. This talk distills that journey into practical lessons for today's practitioners: how military discipline and threat-driven thinking translate into effective ISSO programs, why critical-infrastructure legislation like Bill C-26 will reshape organizational accountability, and how to brief non-technical leadership so cybersecurity gets funded and acted on, not just acknowledged. Attendees will leave with a concrete framework for elevating security from a technical function to a governance priority.
Ian Hill & Connie ‘Sunfire’ Hill | Consultant & Developer at Hitsaru LLC
WordPress powers over 40% of modern websites. Being both well-known and open-source, it is ripe for exploitation. Just because your website was built with WordPress doesn't mean it has to become a victim or a statistic. Ian and Connie Hill will share some details about what WordPress actually is, why it needs protecting, real-world examples of common attacks on WordPress, and some essential steps you can take to reduce the risk to your WordPress website.
Andrew Scott | AI Security Engineer, Founder at Evening Star AI
Cyber teams are beginning to give AI agents access to telemetry, threat intelligence, scanners, ticketing systems, cloud consoles, and incident-response workflows. Before an agent receives that access, it needs rules of engagement: a defined mission, approved targets and data, permitted tools, decision authority, human-approval gates, stop conditions, and an auditable record.
Drawing on Army cyber operations, enterprise security, penetration testing, and AI security research, Andrew introduces a practical framework for governing agents used in threat hunting, vulnerability management, and incident response. He explains how agentic systems expand the attack surface beyond prompt injection and examines failures such as poisoned context, excessive permissions, unsafe action chains, silent goal drift, and untraceable decisions.
Attendees will leave with a reusable checklist for deciding what an AI agent may observe, recommend, execute, and escalate before it receives access to sensitive systems or consequential workflows.
Dr. Sara Rabinovitch, PhD
John Stoner & Josh Mason
Douglas Kaluhiokalani
Tyler Hardy | Principal Cloud Security Engineer, Cybersecurity leader, and doctoral researcher
This is a review of modern academic literature surrounding intrinsic, post-hoc, and mechanistic artificial intelligence explainability. Why does the AI say what it does? We deep dive that in 30 minutes or less.
John Stoner + Tyler Hardy
Want to support VetSec and our efforts to employ veterans in cybersecurity?
Please make a donation today! All donations are tax-deductible.